⚡
Presentation
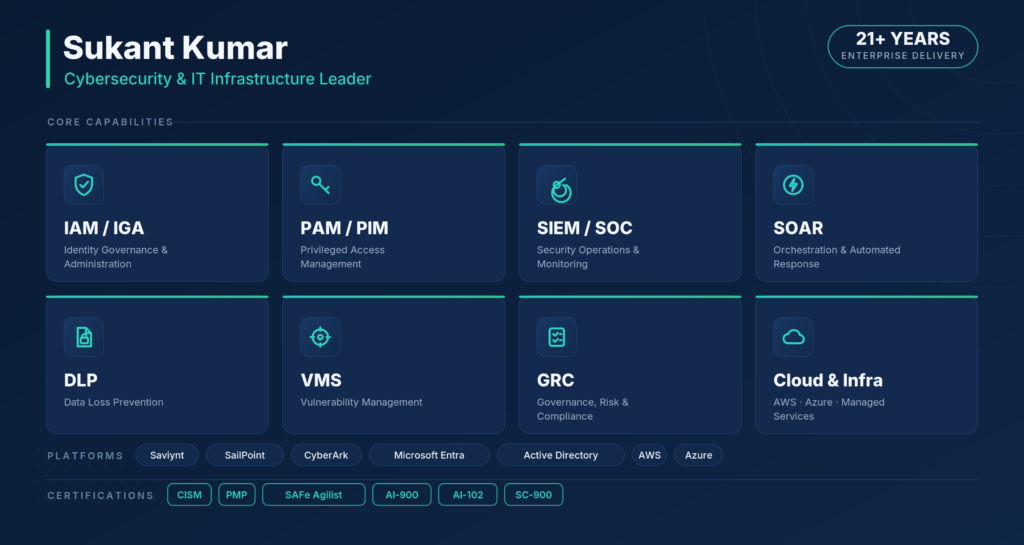
Cybersecurity and IT infrastructure leader with 21+ years delivering enterprise-grade identity, security, and infrastructure programs across large accounts. I specialize in Identity & Access Management and Identity Governance (IAM/IGA) — with hands-on, end-to-end deployment experience across Saviynt, SailPoint, CyberArk, Microsoft Entra, Active Directory, and PAM/PIM — helping organizations design, deploy, and mature their identity security posture.
My work spans the full security and infrastructure stack: IAM/IGA and privileged access (PAM/PIM), SOC/SOAR and SIEM operations, Data Loss Prevention (DLP), vulnerability management (VMS), and Governance, Risk & Compliance (GRC). On the infrastructure side, I lead cloud (AWS, Azure) and enterprise managed-services delivery — bringing programs from design through deployment, operations, and continuous improvement.
I operate at a delivery-leadership level: scoping engagements, owning outcomes, managing teams, and translating complex security requirements into working, audit-ready solutions. Whether you need a specialist to stand up an identity platform, harden your security operations, or bring structure to a governance and compliance program, I bring both the technical depth and the program ownership to see it through.
Certifications: CISM, PMP, SAFe Agilist (SA), and Microsoft AI-900, AI-102, SC-900. MBA in Project Management.
🖼️
Portfolio
🛠️
Offered services
Remote IAM / IGA Implementation & Delivery (Contract)
Hands-on remote delivery for identity and security implementations. I handle end-to-end deployment and configuration work across Saviynt, SailPoint, CyberArk, Microsoft Entra, and Active Directory — i ...
120 $ Per hour
Cybersecurity & Identity (IAM/IGA/PAM) Consulting & Advisory
Senior advisory for organizations designing, deploying, or maturing their identity and security programs. With 21+ years across enterprise accounts, I advise on Identity & Access Management and ...
300 $ Per hour
📋
Background
Senior Director, Delivery
● Own client technology delivery, budget, and vendor relationships across a $15M+ portfolio while partnering with enterprise CIOs/CISOs on governance, operating models, and delivery oversight.
● Extend identity and security principles to enterprise AI/LLM platform adoption — designing secure API gateway patterns, OAuth 2.0/SAML federated identity, and access controls for AI workloads within governed, compliant operating environments.
● Architect enterprise AI-governance and compliance frameworks — embedding responsible-AI guardrails, data-privacy controls, and model access governance aligned to the EU AI Act, NIST AI RMF, and India DPDP Act 2023 — into client GenAI adoption programs.
● Lead steering committee reviews, executive risk reporting, and delivery governance across active client accounts.
● Own client technology delivery, budget, and vendor relationships across a $15M+ portfolio while partnering with enterprise CIOs/CISOs on governance, operating models, and delivery oversight.
● Extend identity and security principles to enterprise AI/LLM platform adoption — designing secure API gateway patterns, OAuth 2.0/SAML federated identity, and access controls for AI workloads within governed, compliant operating environments.
● Architect enterprise AI-governance and compliance frameworks — embedding responsible-AI guardrails, data-privacy controls, and model access governance aligned to the EU AI Act, NIST AI RMF, and India DPDP Act 2023 — into client GenAI adoption programs.
● Lead steering committee reviews, executive risk reporting, and delivery governance across active client accounts.
AI/ML Senior Manager
● Contributed to infrastructure, identity, and security architecture decisions within the Technology for Operations practice for Fortune 500 enterprise modernization programs.
● Partnered with engineering teams on platform stability, secure-by-design patterns, and AI/ML-aligned infrastructure and access-control considerations.
● Partnered with engineering teams on platform stability, secure-by-design patterns, and AI/ML-aligned infrastructure and access-control considerations.
Associate Director – Infrastructure Services
IT Operations & Infrastructure Leadership
● Owned identity governance and access services for a 30,000+ identity estate across Saviynt IGA, CyberArk PAM, SailPoint IGA, Active Directory, M365, and Entra, reducing access certification cycle time by 50% through automation.
● Directed 40+ IT managers, engineers, technicians, and team leads across Service Desk, Active Directory, Entra, Cloud, Messaging, IAM, and SOC-aligned operations.
● Drove on-premises-to-cloud migration and infrastructure modernization (Azure, AWS, hybrid); devised and implemented IT policies, operational standards, and SLA/KPI governance frameworks across the technology portfolio.
Identity Governance & Privileged Access Management
● Owned end-to-end design, build, and delivery of Identity Governance and Administration on Saviynt IGA — implemented from the ground up, replacing legacy identity management for a 30,000+ identity estate — reducing access certification cycle time by 50% through workflow automation.
● Owned hands-on delivery and operations of CyberArk privileged access management (PAM/PIM) — vaulting, session management, and privileged-account governance; carried additional hands-on SailPoint IGA platform experience alongside Saviynt.
● Governed identity federation and Zero Trust access patterns (OAuth 2.0/SAML) across enterprise applications and Active Directory/Entra ID, extending secure identity integration to cloud and SaaS platforms.
Security Operations, GRC & Risk Management
● Built and operationalized 24x7 SOC capability spanning SOAR-driven automation, detection use-case lifecycle, threat intelligence and hunting (CTI/CTH), and incident response — achieving 40% MTTR reduction and 30% playbook automation.
● Established security governance routines: executive risk forums, control-review cadences, exception handling, risk-acceptance workflows, and regulator reporting; owned ISMS-aligned audit readiness for two major UK retail and commercial banking clients operating under regulated financial-services requirements.
● Governed Vulnerability & Exposure Management (VMS) — risk-based prioritization, remediation governance, and SLA improvement — and directed DLP/insider-risk and endpoint security baseline programs across a 30,000+ user environment.
● Led the response and recovery of a major ransomware incident with multi-million-dollar business impact, including credential rotation, access re-certification, privileged-account remediation, and post-incident preventive controls.
Vendor, Budget & Team Leadership
● Controlled IT budget and expenditure reporting across a multi-vendor technology portfolio, delivering $2M+ in annual cost optimization through contract renegotiation and consolidation of redundant services.
● Governed 15+ MSP and technology vendor relationships, including the identity and security ecosystem (Saviynt, CyberArk, SailPoint, Microsoft) — ran service reviews and tracked SLA/KPI performance.
● Built and led a 40+ person IT and security engineering organization — owned hiring strategy, coaching, performance management, and succession planning.
Senior Manager - Technology
● Directed data centre construction, infrastructure design, and network security operations for a global BFSI analytics organization serving US and UK financial institutions; conducted IT risk/vulnerability assessments across business units.
● Managed vendor contracts (Wipro, BT, Dimension Data) and IT asset lifecycle; performed weekly availability analysis and monthly executive risk-posture dashboard reporting.
● Managed vendor contracts (Wipro, BT, Dimension Data) and IT asset lifecycle; performed weekly availability analysis and monthly executive risk-posture dashboard reporting.
Project Lead
● Executed infrastructure modernization and data centre build projects using structured PM methodologies; owned risk/issue registers, governance reporting, and formal project closures.
Service Delivery Manager
● Managed identity and directory services (Windows, Active Directory, DNS) and business-critical server infrastructure of 3,000+ servers for global enterprise clients, including banking and financial services accounts, maintaining 99.9% SLA compliance.
● Administered TSM backup infrastructure; received IBM Stock Options (Long-Term Performance Plan) and multiple technical excellence awards.
● Administered TSM backup infrastructure; received IBM Stock Options (Long-Term Performance Plan) and multiple technical excellence awards.
MBA
MBA in project management
B.SC
Bachelor of Science in Maths and Physics
BCA
Bachelor in Computer Applications
🏅
AI-102
AI-202
🏅
SC-300
SC-300
🏅
SC-900
SC-900
🏅
AI-900
AI-900
🏅
CISM
CISM
🏅
PMP
PMP
🏅
ITIL
ITIL
🇬🇧English 🇮🇳Hindi
🕐
Working hours
Monday ▪ Today
From10h00To21h00
Tuesday
From10h00To21h00
Wednesday
From10h00To21h00
Thursday
From10h00To21h00
Friday
From10h00To21h00
Saturday
Closed
Sunday
Closed
⭐
Reviews
Please sign in as a customer to give your feedback
💬
No reviews yet.
Be the first to share your experience with this professional.