⚡
Presentation
I am a professional IT Specialist with a strong focus on System Administration and Cybersecurity. I provide reliable solutions for setting up and securing your digital infrastructure.
My Expertise:
Operating Systems: Advanced administration of Linux (Ubuntu, Debian, CentOS) and Windows Server.
Windows Ecosystem: Full setup and management of Active Directory, Group Policies (GPO), and Domain Services.
Cybersecurity: System hardening, security audits, and vulnerability assessments.
Networking: Configuration of secure VPNs, firewalls, and monitoring tools.
🛠️
Offered services
📋
Background
Cloud Security Analyst & Red Team Practitioner
Completed intensive professional training at the Higher Academy for AD & Cybersecurity (HAAD). Gained deep practical knowledge in enterprise-level infrastructure management and offensive security.
Key areas of focus:
Active Directory Environment: Deep dive into Windows Server administration, GPO, and domain security.
Linux Systems: Advanced administration and security hardening for Linux-based infrastructures.
Network Security: Designing and securing corporate networks against modern threats.
Security Operations: Practical labs on vulnerability assessment and incident response.
This academic foundation, combined with my international certifications, allows me to provide high-end security services for complex IT environments.
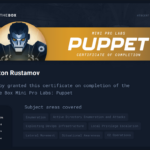
Hack The Box Certificate of Completion: Mini Pro Labs (Puppet)
Hack The Box Mini Pro Labs: Puppet - Certificate of Completion.
Successfully completed a rigorous hands-on laboratory environment focused on compromising modern enterprise infrastructures. This certification validates my technical proficiency in executing complex attack chains.
Core Skills Demonstrated:
DevOps Infrastructure Exploitation: Identifying and leveraging flaws in modern development environments.
Active Directory Enumeration & Attacks: Advanced techniques for mapping and compromising AD domains.
C2 Operations: Setting up and managing Command and Control infrastructure for persistence.
Privilege Escalation & Lateral Movement: Expert-level techniques for moving across networks and elevating access.
Situational Awareness: Analyzing environments to execute precise, stealthy operations.
ID: HTBCERT-D8EA3A33F9
Hack The Box Certificate of Completion: Mini Pro Labs (Mythical)
Hack The Box Mini Pro Labs: Mythical - Certificate of Completion.
Successfully completed an advanced hands-on lab environment focused on enterprise-level exploitation and post-exploitation. This lab demonstrates my proficiency in attacking critical Windows services and databases.
Core Skills Demonstrated:
AD Certificate Services (AD CS) Exploitation: Mastering attacks against PKI infrastructure in Active Directory.
MSSQL Database Attacks: Specialized techniques for compromising SQL servers and escalating privileges.
Advanced Lateral Movement: Navigating complex networks using situational awareness and C2 frameworks.
Persistence: Establishing long-term access within secure infrastructures.
ID: HTBCERT-DA3B942832
Certified Kubernetes Red Team Analyst (K8s-RTA)
Certified Kubernetes Red Team Analyst (K8s-RTA) by CyberWarfare Labs.
I am a highly specialized security professional focused on offensive security within containerized environments. This certification validates my expertise in identifying and exploiting misconfigurations in Kubernetes clusters.
Core Skills Demonstrated:
Container & Cluster Exploitation: Gaining initial access to K8s clusters, pod escapes, and lateral movement between containers.
RBAC & Secret Management: Exploiting weak Role-Based Access Control and mismanaged secrets.
Cloud-Native Security: Testing the resilience of orchestration platforms against modern attack vectors.
Post-Exploitation: Demonstrating high-impact scenarios within complex cloud infrastructures.
ID: K8s-RTA-693429d27b627b6c7f108bca
Multi-Cloud Red Teaming Analyst
Multi-Cloud Red Teaming Analyst by CyberWarfare Labs.
Advanced certification validating my ability to conduct red team operations across complex multi-cloud environments (AWS, Azure, GCP). I am an expert in identifying misconfigurations and exploiting cross-cloud trust relationships to secure enterprise assets.
Core Skills Demonstrated:
Cross-Cloud Exploitation: Executing attack chains that span multiple cloud providers.
Cloud Identity & Access Management (IAM): Exploiting IAM misconfigurations and performing privilege escalation within multi-cloud tenants.
Cloud-Native Attack Vectors: Simulating real-world threats against serverless, containerized, and managed services.
Strategic Cloud Hardening: Providing advanced recommendations for multi-cloud security architecture and defense.
ID: 692dc3ef524427687605ae55
Certified Web Application Red Teaming Analyst (WEB-RTA)
Certified Web Application Red Teaming Analyst (WEB-RTA) by CyberWarfare Labs.
This certification validates my advanced skills in offensive web security and penetration testing. I have been trained to simulate real-world cyber attacks using the latest tactics, techniques, and procedures (TTPs).
Core competencies demonstrated:
Advanced Reconnaissance: In-depth mapping of web infrastructures to find hidden entry points.
Vulnerability Exploitation: Skilled in exploiting OWASP Top 10 vulnerabilities (SQLi, XSS, SSRF, IDOR, etc.).
Red Team Methodologies: Simulating Advanced Persistent Threats (APT) to test the resilience of web defenses.
Security Assessment: Providing comprehensive reports on how to patch vulnerabilities and harden system security.
ID: WEB-RTA-692adce77b627b6c7f0d1641
Certified Active Directory Red Team Specialist (AD-RTS)
Certified Active Directory Red Team Specialist (AD-RTS) by CyberWarfare Labs.
I am an expert in compromising and securing complex Windows Active Directory environments. This certification proves my ability to perform advanced reconnaissance, exploit misconfigurations, and simulate stealthy attacks within enterprise networks.
Core Skills Demonstrated:
Active Directory Exploitation: Kerberoasting, AS-REP Roasting, Golden/Silver Ticket attacks.
Lateral Movement & Privilege Escalation: Moving across enterprise networks to gain high-level access.
GPO & ACL Analysis: Identifying security flaws in Group Policies and Access Control Lists.
Persistence & Stealth: Establishing long-term presence while bypassing modern security defenses.
ID: ADRTS-692a66ba4ae64839616a4b0d
Certified Red Team Infra Dev (CRT-ID)
Certified Red Team Infra Dev (CRT-ID) by CyberWarfare Labs.
Specialized certification focused on the design, development, and deployment of resilient Red Team infrastructures. This validates my ability to build stealthy command-and-control (C2) systems and advanced attack platforms.
Core Skills Demonstrated:
Infrastructure Automation: Building scalable and disposable attack infrastructures using modern DevOps tools.
C2 Infrastructure Design: Developing stealthy communication channels with redirectors, payload delivery, and domain fronting.
Evasion & OpSec: Implementing advanced operational security measures to bypass detection and analysis.
Backend & Frontend Security Development: Creating secure and efficient management platforms for offensive operations.
ID: CRT-ID-6925e8d4e0d2558f541a6f44
Certified Red Team Analyst (CRTA)
Certified Red Team Analyst (CRTA) by CyberWarfare Labs.
This certification demonstrates my comprehensive understanding of Red Team operations and methodologies. I am trained to simulate realistic attack scenarios against entire organizational infrastructures, focusing on stealth, evasion, and strategic exploitation.
Core Skills Demonstrated:
Red Team Methodology: Planning and executing end-to-end attack simulations.
Advanced Reconnaissance & Weaponization: Crafting specialized payloads and identifying entry points.
Evasion Techniques: Bypassing modern security controls (Antivirus, EDR, Firewall).
Post-Exploitation & Reporting: Conducting thorough analysis after compromise to provide actionable security insights.
ID: CRTA-6924be899f54e3df3cb187c9
🇬🇧English
🕐
Working hours
Monday ▪ Today
From08h00To18h00
Tuesday
From08h00To18h00
Wednesday
From08h00To18h00
Thursday
From08h00To18h00
Friday
From08h00To18h00
Saturday
Closed
Sunday
Closed
⭐
Reviews
Please sign in as a customer to give your feedback
💬
No reviews yet.
Be the first to share your experience with this professional.