
⚡
Presentation
As an Information Security student, I specialize in penetration testing, malware analysis, and digital forensics, with a strong focus on uncovering how attacks actually work and how to stop them. I’ve built hands-on experience working in realistic lab environments (Kali Linux, FLARE VM, Metasploitable), simulating attacks, analyzing threats, and developing defensive strategies.
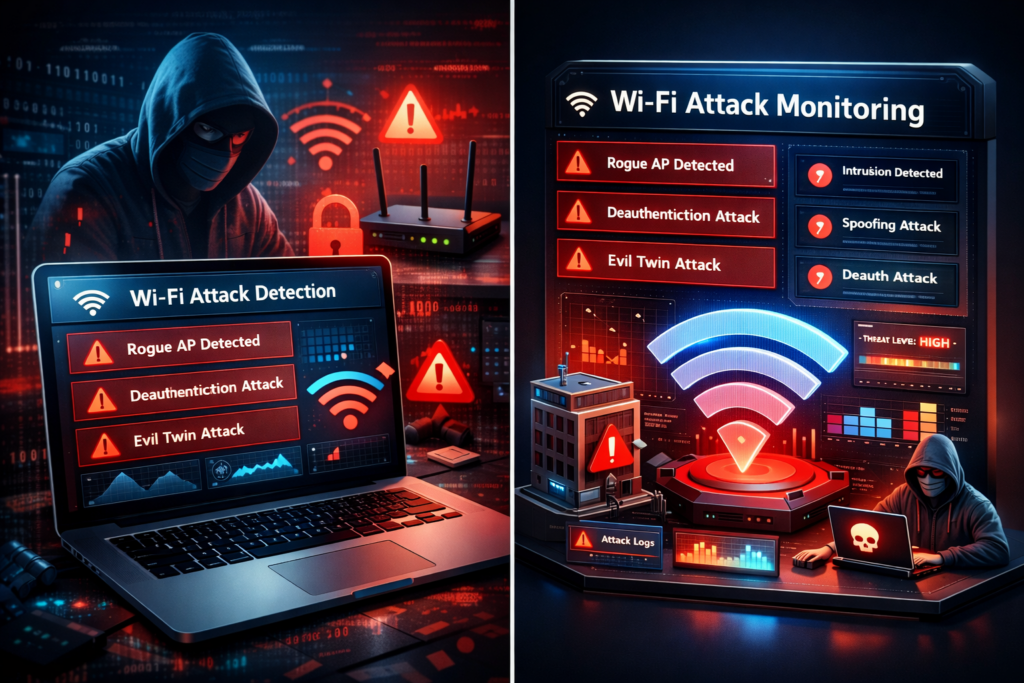
My work goes beyond theory. I’ve analyzed advanced malware like Bumblebee using both static and dynamic techniques, performed web application reconnaissance on platforms like inDrive, and designed Wi-Guard — an AI-powered Wi-Fi attack detection system that identifies threats like Evil Twin and deauthentication attacks in real time.
I’m highly comfortable with tools like Nmap, Metasploit, Wireshark, Burp Suite, and Aircrack-ng, and I write custom Python scripts to automate security tasks and improve efficiency. Whether it’s finding vulnerabilities, analyzing malicious behavior, or investigating digital evidence, I focus on delivering clear, actionable results.
My work goes beyond theory. I’ve analyzed advanced malware like Bumblebee using both static and dynamic techniques, performed web application reconnaissance on platforms like inDrive, and designed Wi-Guard — an AI-powered Wi-Fi attack detection system that identifies threats like Evil Twin and deauthentication attacks in real time.
I’m highly comfortable with tools like Nmap, Metasploit, Wireshark, Burp Suite, and Aircrack-ng, and I write custom Python scripts to automate security tasks and improve efficiency. Whether it’s finding vulnerabilities, analyzing malicious behavior, or investigating digital evidence, I focus on delivering clear, actionable results.
📋
Background
🇬🇧English
🕐
Working hours
Monday
From08h00To18h00
Tuesday
From08h00To18h00
Wednesday
From08h00To18h00
Thursday
From08h00To18h00
Friday
From08h00To18h00
Saturday
Closed
Sunday ▪ Today
Closed
⭐
Reviews
Please sign in as a customer to give your feedback
💬
No reviews yet.
Be the first to share your experience with this professional.