⚡
Presentation
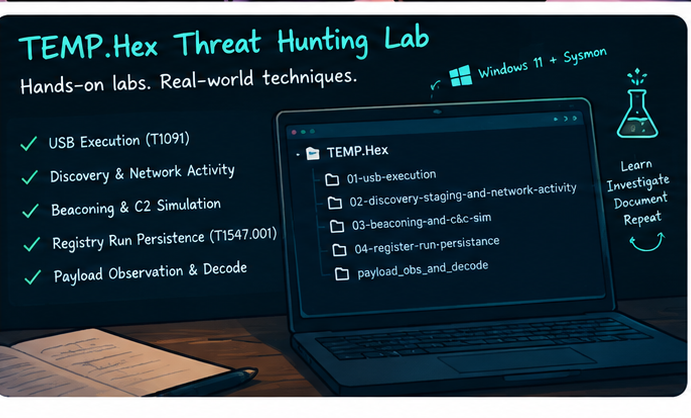
I provide cybersecurity threat hunting and detection services focused on identifying suspicious activity, validating security telemetry, and improving detection coverage across enterprise environments.
My experience includes campaign-based threat hunting across the attack lifecycle using Microsoft Sentinel, Microsoft Defender XDR, CrowdStrike Falcon, Google Threat Intelligence (GTI), KQL, Sysmon, and MITRE ATT&CK.
Services I can provide:
Threat hunting based on IOCs, TTPs, intelligence, behaviors, and attack hypotheses
KQL query development and optimization for Microsoft Sentinel and Defender
Threat intelligence research, IOC enrichment, and campaign profiling
MITRE ATT&CK mapping and detection-gap analysis
Detection logic and security use-case development
Windows/Sysmon telemetry analysis and investigation
Suspicious process, network, authentication, persistence, and execution activity analysis
Ransomware and targeted-intrusion hunting
Hunt findings, technical reports, and actionable recommendations
I focus on turning raw security telemetry and threat intelligence into clear hypotheses, practical detections, and actionable findings that security teams can use to improve their defensive coverage.
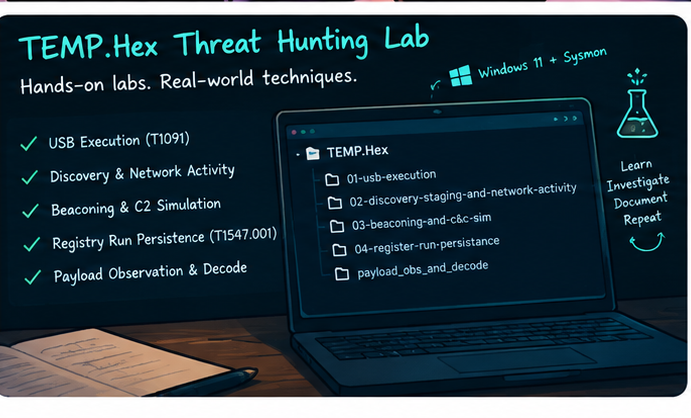
I can also develop structured threat-hunting case studies and detection content
My experience includes campaign-based threat hunting across the attack lifecycle using Microsoft Sentinel, Microsoft Defender XDR, CrowdStrike Falcon, Google Threat Intelligence (GTI), KQL, Sysmon, and MITRE ATT&CK.
Services I can provide:
Threat hunting based on IOCs, TTPs, intelligence, behaviors, and attack hypotheses
KQL query development and optimization for Microsoft Sentinel and Defender
Threat intelligence research, IOC enrichment, and campaign profiling
MITRE ATT&CK mapping and detection-gap analysis
Detection logic and security use-case development
Windows/Sysmon telemetry analysis and investigation
Suspicious process, network, authentication, persistence, and execution activity analysis
Ransomware and targeted-intrusion hunting
Hunt findings, technical reports, and actionable recommendations
I focus on turning raw security telemetry and threat intelligence into clear hypotheses, practical detections, and actionable findings that security teams can use to improve their defensive coverage.
I can also develop structured threat-hunting case studies and detection content
🖼️
Portfolio
🛠️
Offered services
📋
Background
🇬🇧English 🇮🇳Hindi
🕐
Working hours
Monday
From08h00To18h00
Tuesday
From08h00To18h00
Wednesday
From08h00To18h00
Thursday
From08h00To18h00
Friday
From08h00To18h00
Saturday
Closed
Sunday ▪ Today
Closed
⭐
Reviews
Please sign in as a customer to give your feedback
💬
No reviews yet.
Be the first to share your experience with this professional.